AI Security: What Every Builder Must Know Before They Ship
Join Nahid Farady, PhD (Principal Tech Lead, AI Security · Microsoft) for a free live session.
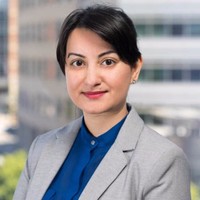
Nahid Farady, PhD
Principal Tech Lead, AI Security · Microsoft
⭐ 4.9 / 5
You're one prompt injection away from a breach. Most AI teams don't know it yet.
Traditional security training doesn't cover LLM attack surfaces. Prompt injection, indirect RAG poisoning, jailbreaks, data leakage through model outputs — these are live threats in production AI systems right now. In 4 weeks, you'll learn to map, harden, and defend AI systems the way the top 1% of security practitioners do — and make justified ship/hold decisions backed by real risk analysis.
You walk away with
What You'll Learn
Map Your AI Attack Surface
Identify prompt injection, jailbreaks, indirect RAG poisoning, and data leakage vectors specific to your architecture — not generic checklists.
Harden Inputs & Prompts
Build layered defenses: input validation, system prompt hardening, and semantic classifiers. NOT single-layer string matching that's trivially bypassed.
Control Outputs with Guardrails
Implement PII detection, hallucination checks, and content filters. Evaluate real tools (Guardrails AI, NeMo) on precision vs. latency tradeoffs.
Ship/Hold Decision Framework
Run a structured AI security audit and make a justified ship/hold call with documented cost vs. risk tradeoffs your stakeholders can act on.
Who Is This For?
This course is designed for:
Security Engineers
Moving into AI systems who need to understand LLM-specific attack surfaces that traditional AppSec training doesn't cover.
AI Engineers & Builders
Shipping LLM apps, RAG pipelines, and agents who need to stop treating security as someone else's problem.
AI PMs & Tech Leads
Making ship/hold calls on AI features who need a rigorous security review framework — not vibes.
Course Outline
4 weeks · 3 sessions per week
Projects You'll Ship
Leave with real work to show, not just a certificate.
AI Threat Model
A 1-page attack surface map for a real AI system — input vectors, RAG risks, output leakage, and prioritized defense plan. Reusable as a starting template for any LLM system you build.
Prompt Hardening Implementation
A layered input defense with benchmarked results — tested against real prompt injection and jailbreak attempts. Documented and portable to any production system.
AI Security Review + Ship/Hold Decision
A full security audit of a real AI system with CI/CD gates, residual risk documentation, and a stakeholder-ready ship/hold recommendation. The artifact that justifies deployment decisions.
Your Instructors
Nahid Farady, PhD
Principal Tech Lead, AI Security · Microsoft
⭐ 4.9 / 5
Nahid Farady holds a PhD from Virginia Tech and leads AI security, privacy, and responsible AI at Microsoft Copilot. Previously at Google Cloud — where he built privacy-preserving ML and DLP systems — and Capital One CyberML — where he led threat modeling and insider threat detection for ML applications — Nahid brings 10+ years of hands-on experience securing AI systems at scale. He is an Adjunct Professor at UC Berkeley School of Information.
What Students Say
⭐⭐⭐⭐⭐
"Week 1 alone changed how I think about our entire AI stack. We had three prompt injection vulnerabilities I didn't know existed. Fixed all of them by Week 2."
Derek Thompson
AI Engineer · Cloudflare
⭐⭐⭐⭐⭐
"The guardrail tool evaluation framework is something I've never seen taught anywhere. We saved weeks of benchmarking time and made a better decision."
Ashley Morgan
Security Engineer · Okta
⭐⭐⭐⭐⭐
"The Ship/Hold framework in Week 4 is now standard in our AI release process. It's the first time our security reviews have actually influenced deployment decisions."
Nathan Brooks
Tech Lead · Databricks
Course Schedule
All sessions are instructor-led and live. Recordings available within 24 hours.
SUNDAY
9:00 AM PDT
Live ClassDeep dive with live red-teaming, tool demos, and adversarial exercises. Hands-on every session.
WEDNESDAY
6:00 PM PDT
Lab SessionStructured A vs B lab. Compare defenses, evaluate tools, and make real decisions with instructor guidance.
THURSDAY
6:00 PM PDT
Build & ShipBuild and test your weekly deliverable. Peer review and instructor feedback before you submit.
Frequently Asked Questions
Related reading
The JD-backed research behind this course — from Dexity Intel.
The Cybersecurity + AI Career Path in 2026 →How far do you want to go?
Start free to experience our offering, choose the program length you would want to commit to.
You build. Nobody demos at you.
Every session is follow-along — you build the thing yourself while a practitioner works beside you. That is why the hours look long: they are yours to build in, with an expert on hand to guide you. None of it is a traditional lecture.
In the session, you'll: